

Configure Ranger User Sync
Overview
Ranger User Sync is an optional Ranger component that allows you to keep the list of imported users and groups in Ranger up to date. For example, if an imported user was deleted in the source system, with a configured User Sync, it will become hidden in Ranger. It synchronizes users when Ranger is imported into a cluster from a preinstalled ADPS cluster (see the Overview section in Ranger plugins for ADH). After the import, Ranger will synchronize users periodically, by default — once an hour.
|
NOTE
The default search mode looks for groups first and adds users based on their group membership. To change it so that the users are looked up first and groups are added based on the users found, activate the Show advanced switch in the configuration menu and set the ranger.usersync.group.search.first.enabled parameter to false.
|
LDAP sync configuration
Additionally to the default sync method via importing Ranger into a cluster, you can add an LDAP sync source. To do that, follow the steps below:
-
On the Clusters page, click the name of your ADPS cluster, head to the Services tab, and click Ranger.
-
In the configuration parameters, find LDAP sync source for User synchronizer and activate it. After that, fill in the LDAP parameters (see Configuration parameters → Ranger → LDAP sync source for User synchronizer) and click Save.
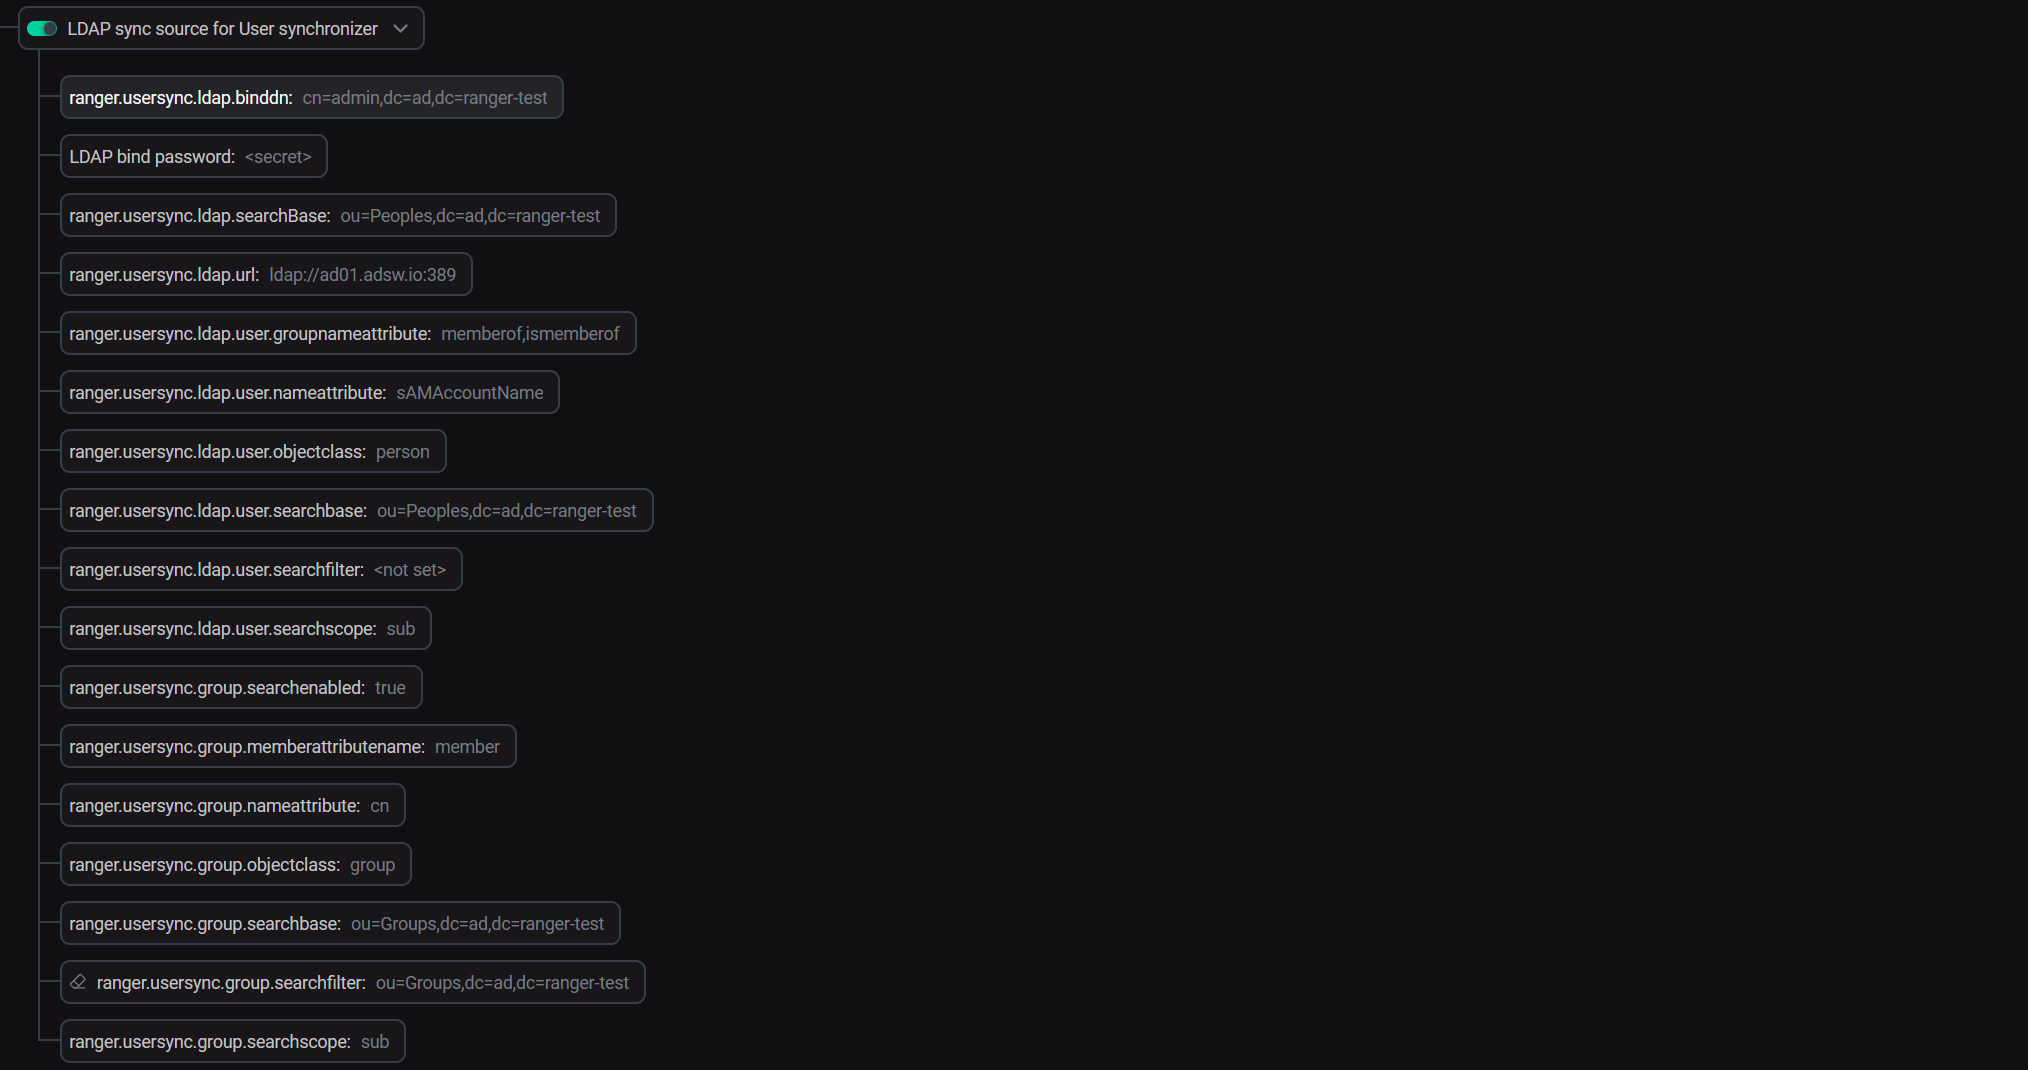 Example of the right LDAP parameters
-
Restart Ranger. The synchronized users/groups will appear on the relevant tabs with their source being
LDAP/AD.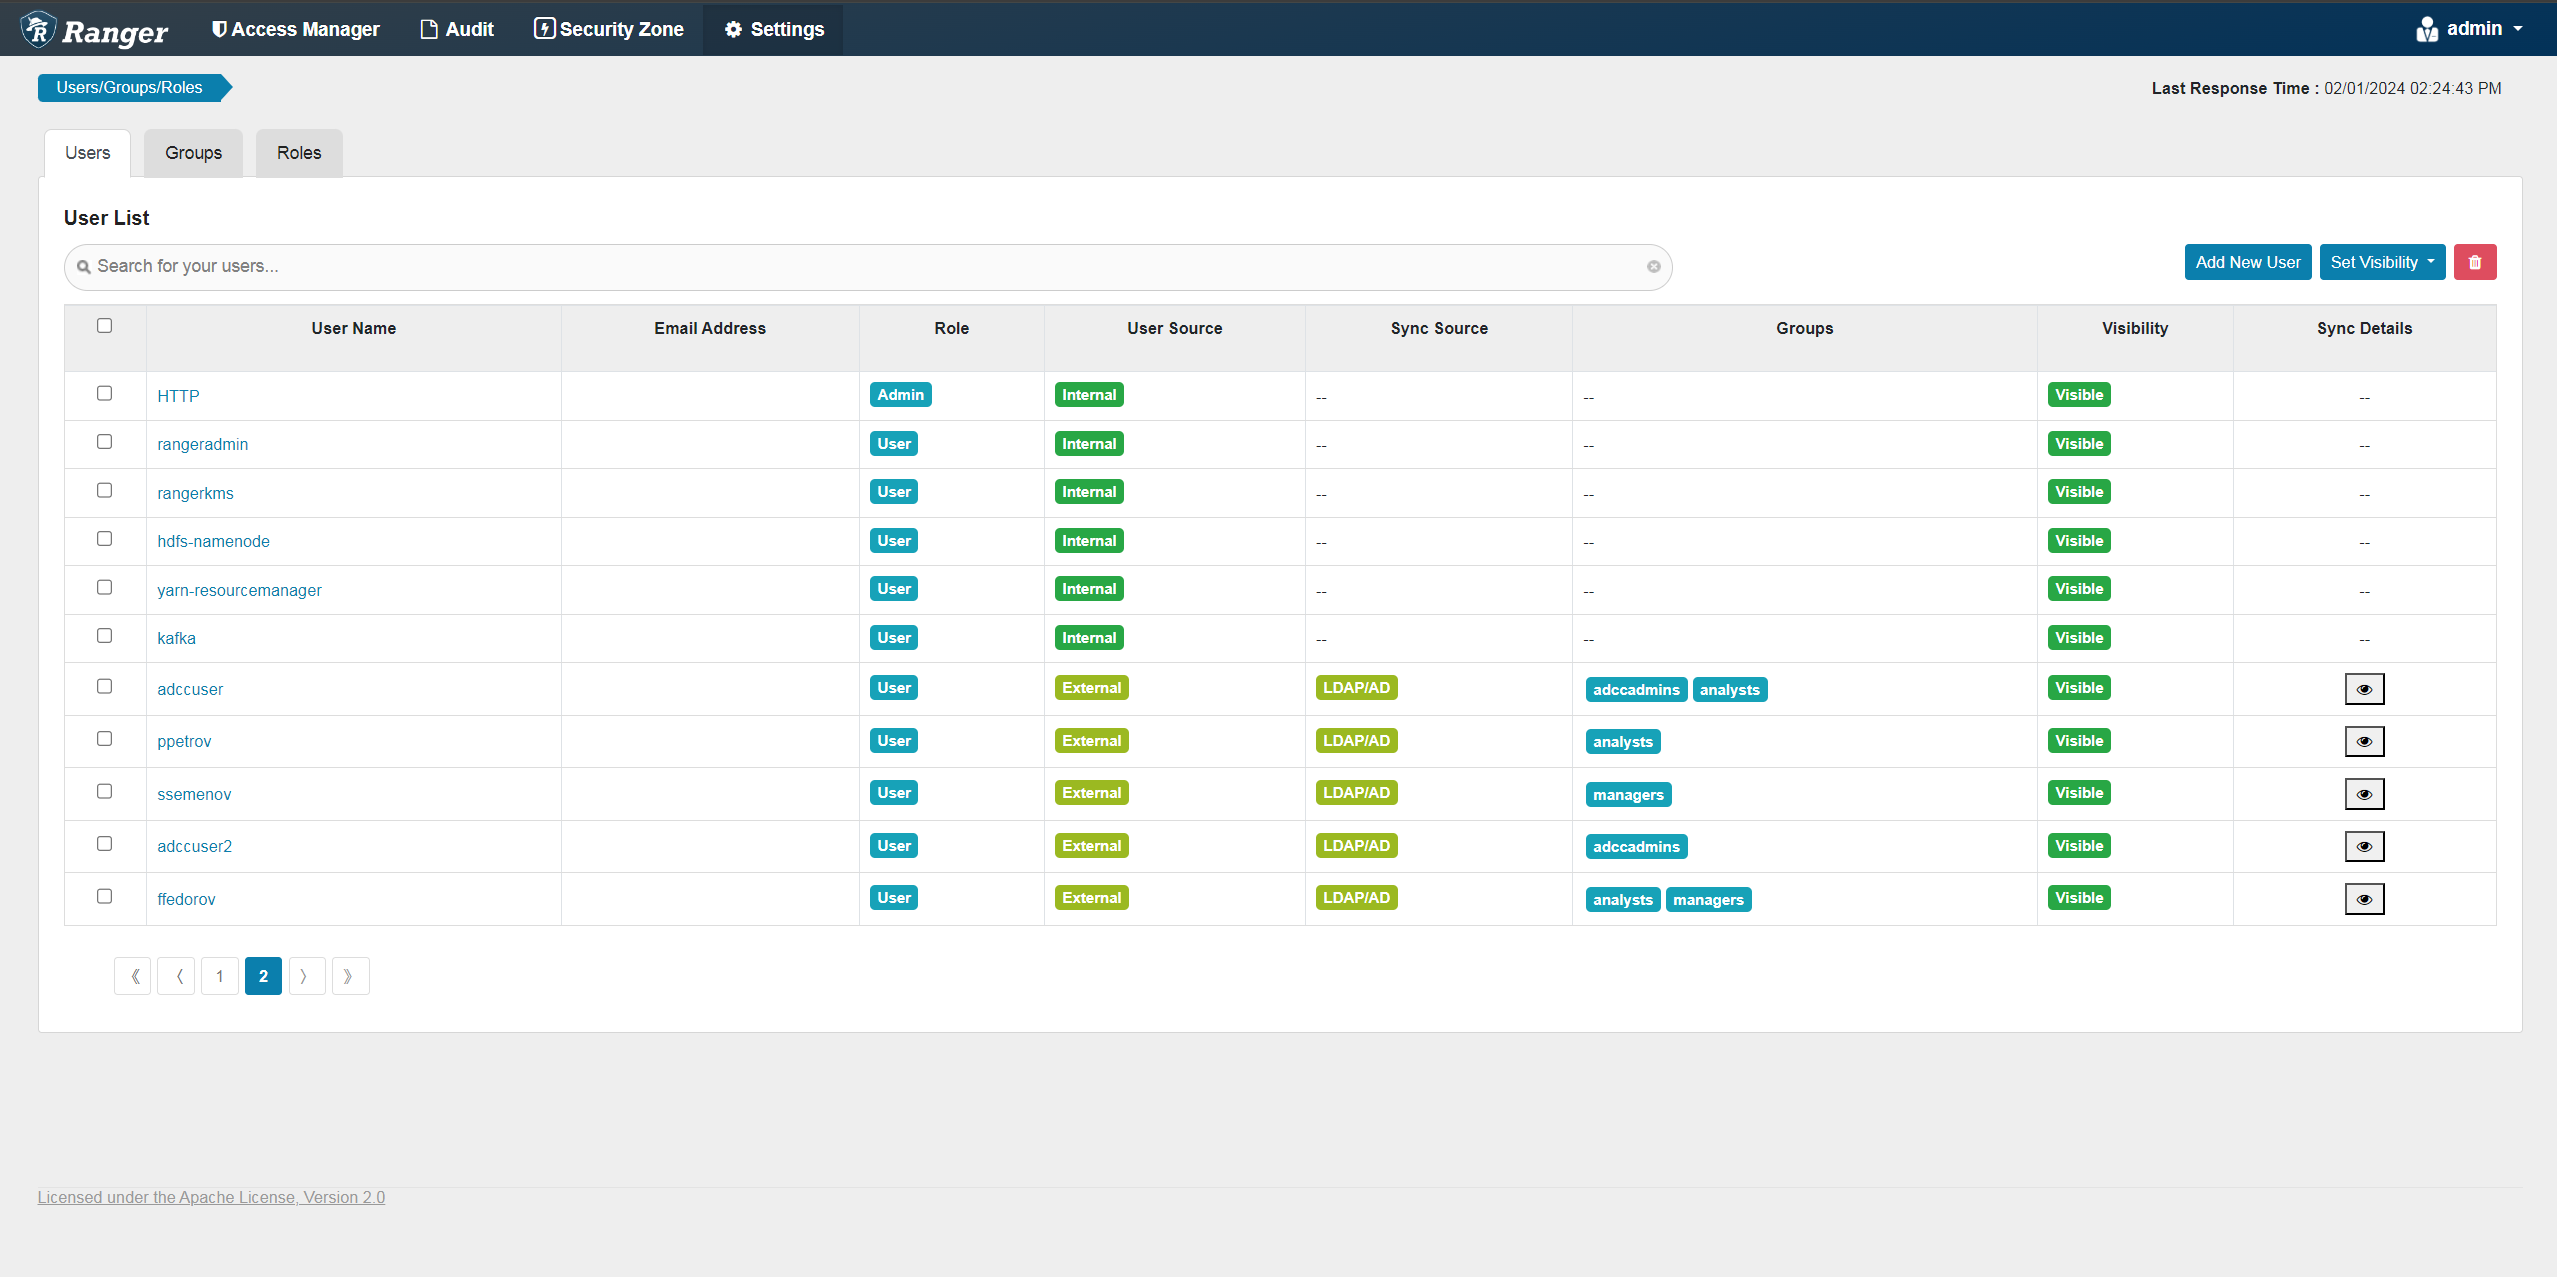 LDAP synchronized users
 LDAP synchronized users
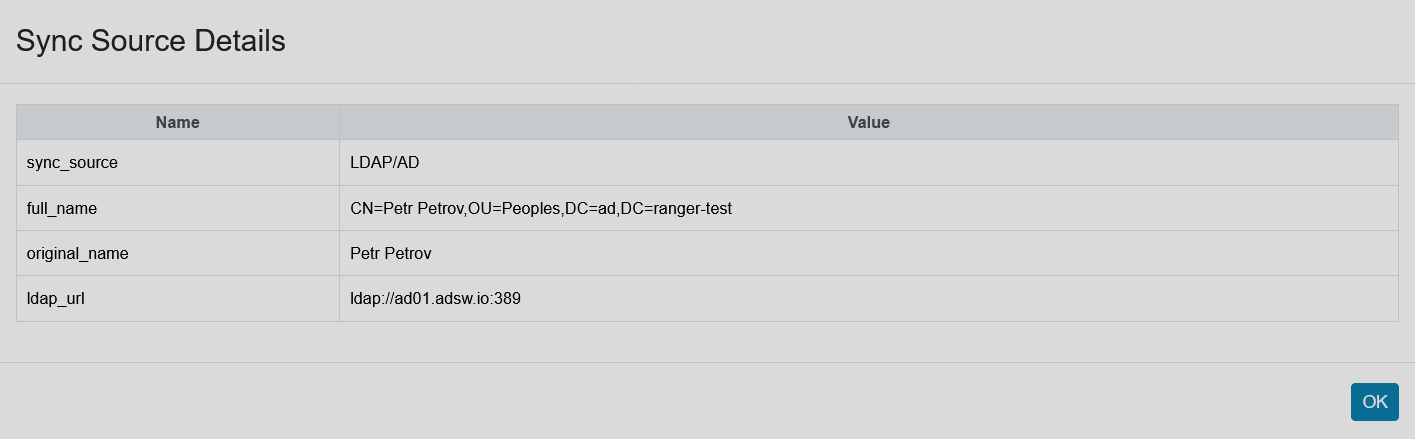
You can find special data on users/groups syncronized from external systems in the Sync Details column of the Users/Groups table. For example, users from Unix have parameters like sync_source, full_name, and original_name. The LDAP users have the forementioned and ldap_url, also their full_name is a DN.
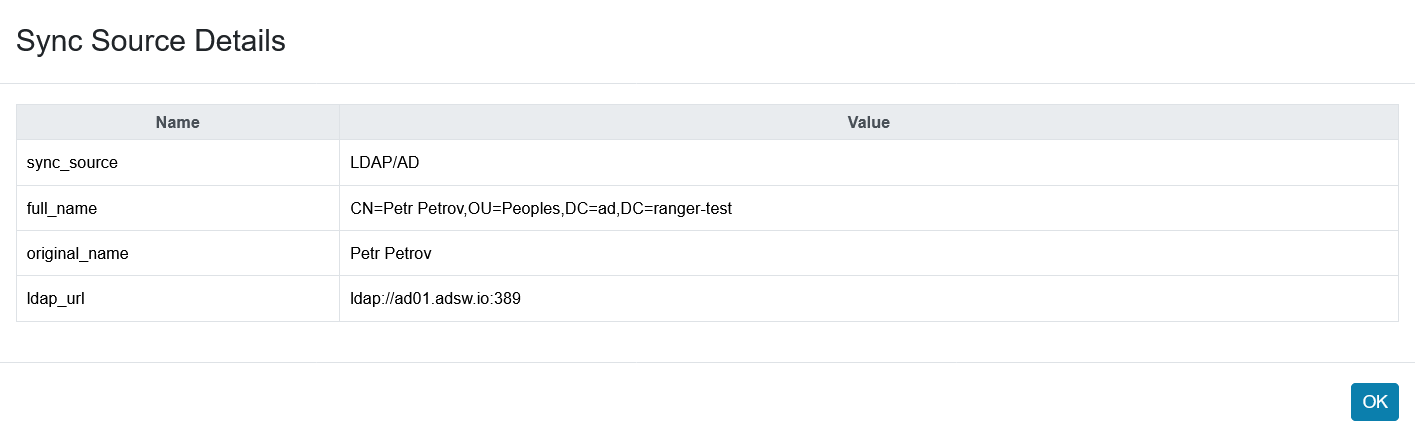
Now, you can manage policies for the imported entities.